

A certificate check fails although the certificate is valid — for anyone who sees a green padlock in the browser while InfraNest flags a problem, or an SSL monitor reports the site as down.
#Overview
- Browsers are forgiving: they fill in missing pieces and remember what they saw before on other sites.
- Our checks, along with apps, payment providers and other servers that connect to your site, are not forgiving.
- When InfraNest disagrees with your browser, it's usually seeing exactly what those other visitors see.
#Find which check fails
- Go to Certificates and open the certificate.
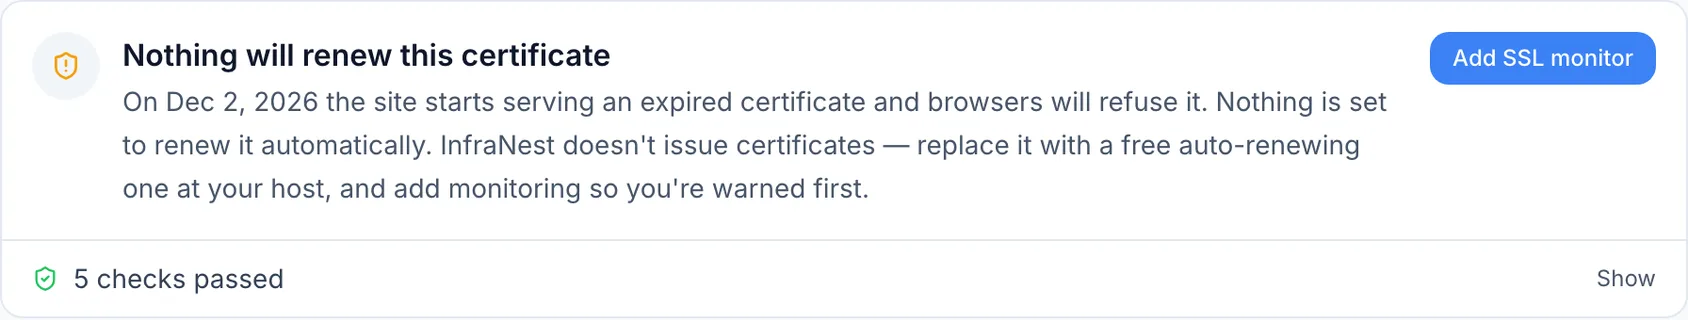
- Check Security posture at the top — it lists only the checks that need attention. Select a row to read what it means and what to do.
If it's an SSL monitor that's down instead, open the monitor under Monitoring. Its message is less specific — Couldn't establish a secure (SSL/TLS) connection, or SSL certificate problem for a website monitor. Either way, open the certificate as above to find out which part failed.
#Fix an incomplete certificate chain
If Chain says Missing intermediate, your server is sending its own certificate but not the one that links it to a certificate authority browsers trust. Browsers often remember that piece from another site, so they don't notice — apps and our checks do.
- Select View chain.
- Open the How to fix this panel — it links to the missing intermediate where the issuer publishes it.
- Add the intermediate to your server's certificate file (usually called the bundle or full chain).
- Restart the web server. Most hosts and control panels have a dedicated field for this.
#Fix a missing address on the certificate
If Hostname says The site's address isn't on the certificate, the certificate doesn't list the exact address being checked. For example, if the monitor checks www.example.com but the certificate only covers example.com, browsers will warn about it even if you never visit that address.
- Either point the monitor at an address the certificate covers,
- Or get a certificate that includes the address you need.
NoteA certificate for
*.example.comcoverswww.example.combut notexample.comitself, and notshop.eu.example.com.
#Resolve a different certificate being served
Your site may serve different certificates to different visitors. This happens when:
- the address points at several servers, and one of them still has an old certificate;
- the site has an IPv6 address, and the server behind it was never given the new certificate;
- a load balancer or CDN sits in front, and its certificate is not the one on your server;
- the server hosts several sites and hands out a default certificate for an address it doesn't recognise.
When InfraNest sees a different certificate at an address you watch, you get a Certificate changed alert, and the other certificate appears as its own row on the Certificates page.
- Open that row to see which certificate our check received.
- Install the right certificate on the server or service that's handing it out.
#Fix an issuer not on your CAA list
If CAA says Issuer not authorized by the domain's CAA policy, your DNS has a rule naming which companies may issue certificates for your domain, and this certificate's issuer isn't on it. The certificate still works, but your next renewal may be refused.
- Either add the issuer to the rule with Manage CAA,
- Or check whether you expected this certificate at all.
#Check again after fixing it
- For a monitor, select Run now on the monitor's page.
- For a certificate without a monitor, go to Certificates, select Add certificate, choose Scan an endpoint, enter the address, and select Scan. The existing certificate is updated.
TipIf you don't check manually, every address is scanned again once a day.
Was this article helpful?
Thanks for your feedback!
Thanks, this goes straight to the docs team.